Compliance & Advisory Services
PatientLock offers a broad range of Advisory Services designed for healthcare organizations, including Virtual Chief Information Security Officer (vCISO), NIST CSF and HIPAA Compliance, Security Risk Assessments, HITRUST and SOC2 Readiness, GAP Assessments, and Incident Response (IR).
vCISO
Virtual Chief Information Security Officer
Healthcare cybersecurity and compliance can be complex. A full-time CISO is a luxury few organizations can afford, but qualified information security leadership is a must. So, what do you do?
A Virtual Chief Information Security Officer (or vCISO) provides the necessary leadership, strategic planning oversight, and guidance required to achieve compliance and minimize security risk to a healthcare organization.
Gap / Baseline Assessments
Identify Your Gaps and Roadmap to Compliance
Achieving readiness or certification on a regulation or framework typically involves a gap assessment. We conduct your gap assessment and provide you with a report and remediation roadmap for frameworks & regulations such as ISO 27001, SSAE18 SOC2, PCI-DSS, NIST-CSF, and many more.
NIST Compliance
Gap Assessment & Implementation Support
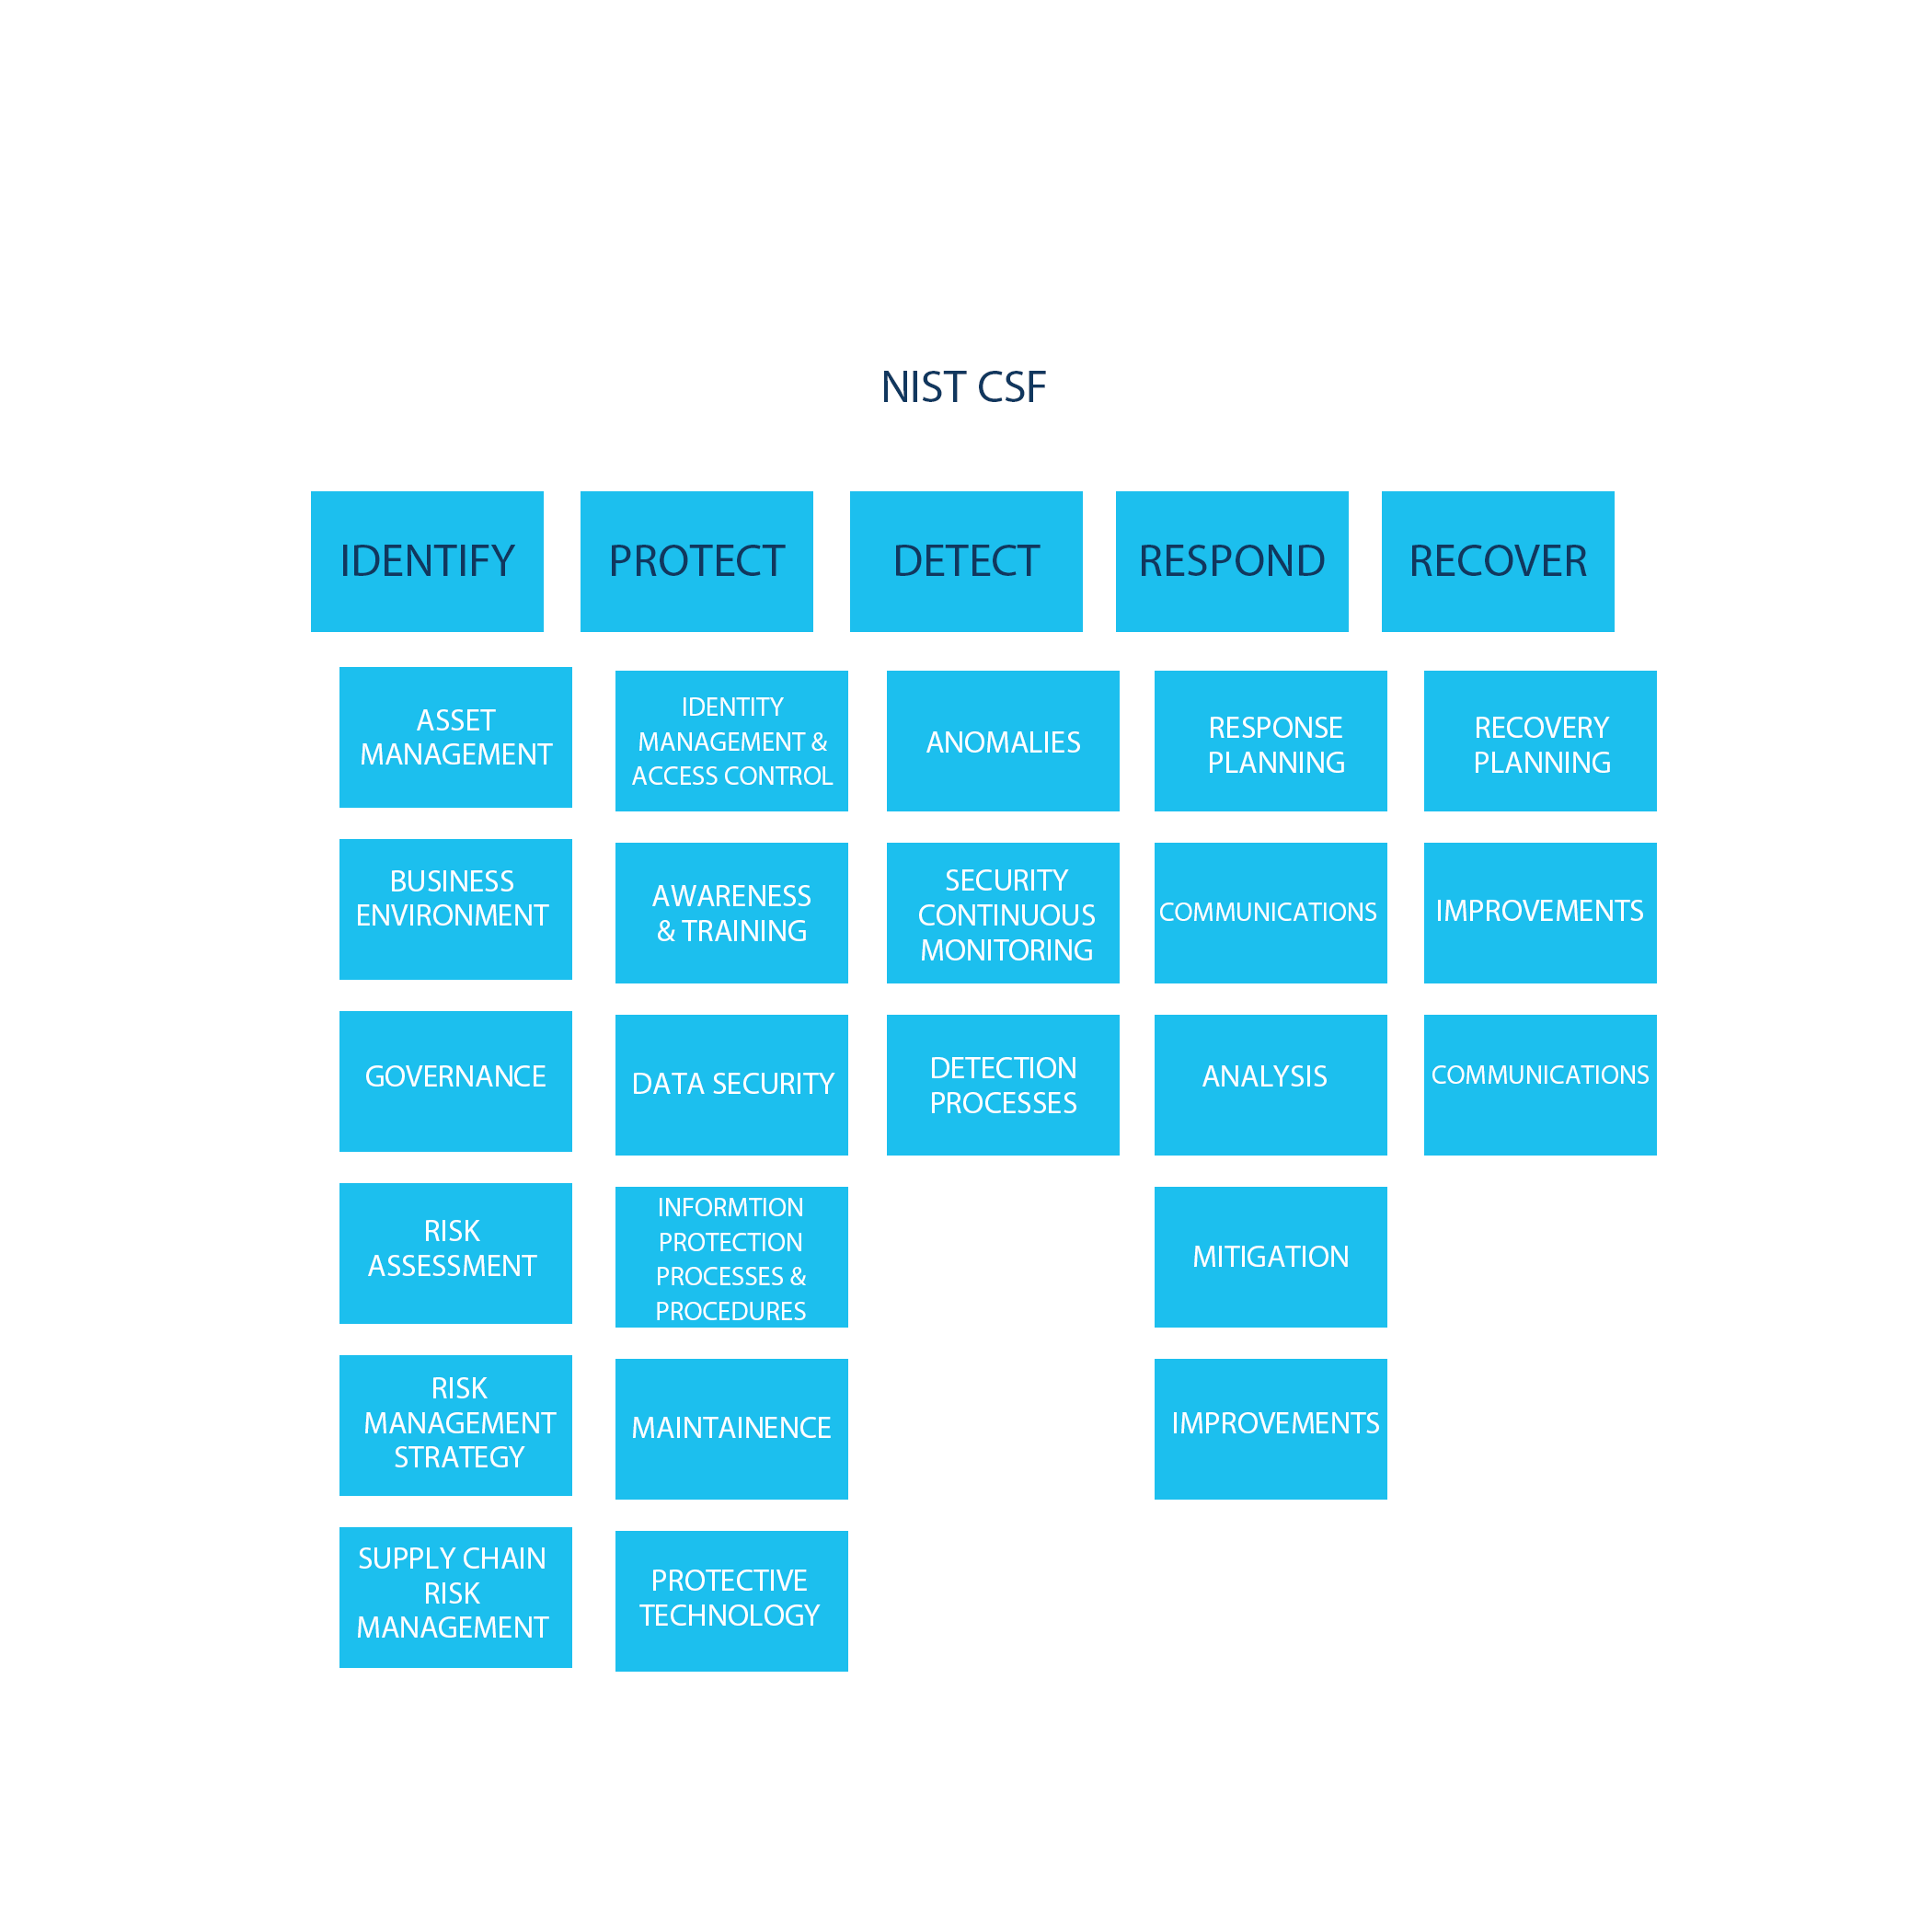
The National Institute of Standards and Technology (NIST) promotes a Cybersecurity Framework (CSF) to enable organizations to better manage and reduce cybersecurity risk.The NIST CSF consists of five core functions – Identify, Protect, Detect, Respond, and Recover. We assess organizations against the five core functions and their categories. This assessment reveals gaps between the framework and the client’s actual security program. Addressing these gaps enables clients improve their cybersecurity posture by implementing a robust, comprehensive cybersecurity framework.
PCI Compliance
Painless Payment Compliance Support
Depending on where you are in your compliance journey, you may be familiar with the Payment Card Industry Data Security Standard (PCI DSS). The PCI DSS is a global standard by the PCI Council that provides a baseline of people, process and technology requirements designated to protect payment data and facilitate consistent data security measures.
PatientLock follows a comprehensive approach to assess and maintain your PCI DSS compliance and certification. Our highly qualified team with years of experience in this area will take the right steps needed to ensure your compliance.
CMMC Compliance
Get Ready for CMMC 2.0 Compliance
PatientLock provides CMMC readiness services to healthcare organizations on their path to certification against the CMMC standard.
HIPAA Risk Assessment
HIPAA Compliance Just Got Easier
PatientLock walks you through every step of the HIPAA process, from assessment to implementation and maintenance, telling you exactly what you need to meet expectations. Find out why hundreds of healthcare organizations trust our HIPAA Compliance services.
Our team of cybersecurity and compliance experts simplify HIPAA compliance into a few key steps — saving you time and limiting employee stress while making sure you stay compliant.
Incident Response (IR)
Be Prepared for Your Next Cyber Incident
Incident response is the systematic approach in which an organization handles a cyber incident or a breach. At a minimum, every organization must have a clear and comprehensive incident response plan outlining roles and responsibilities, process and procedures in the event of a cyber incident. Every person involved in executing the incident response must be trained and should have participated in a series of tests of the plan.
PatientLock is your trusted partner in incident response planning and testing. We work with you in the end-to-end process for incident response.
HITRUST Readiness
HITRUST CSF Framework Readiness Service
Achieve your objective in a timely and efficient manner with PatientLock’s HITRUST Readiness Services.
PatientLock will walk you through a Readiness Assessment for the HITRUST CSF Framework, remediate the gaps, and prepare for a successful, certifiable HITRUST Assessment.
HITRUST Readiness is designed to help you achieve HITRUST CSF Framework validation and compliance with regulatory requirements applicable to healthcare organizations.
Penetration Testing
Identifying and Remediating Vulnerabilities Before They’re Exploited
Penetration testing is a key cybersecurity process where certified professionals simulate authorized cyberattacks to uncover vulnerabilities in your systems, applications, and networks—before threat actors can exploit them.
In today’s evolving threat landscape, healthcare organizations face increased targeting due to the high value of protected health information (PHI). Penetration testing provides a proactive defense strategy that introduces critical human analysis into your risk management efforts. This tailored assessment aligns with frameworks like HIPAA, NIST CSF, and cyber insurance requirements—
Network Security Assessment
Comprehensive Network Analysis
Network Security Assessments are a critical component of maintaining the integrity and confidentiality of your organization’s data and assets. Our team of experts will perform a thorough analysis of your network infrastructure, identifying any potential weaknesses or vulnerabilities. This includes examining your firewalls, routers, switches, and other networking devices to ensure they are properly configured and protected against external threats.
Proactively mitigate risks and protect your business from cyberattacks, data breaches, and other security incidents. Our assessment report will provide recommendations for improving your network security, and our team will work with you to implement these changes and ensure your network is secure.
vCISO
Virtual Chief Information Security Officer
Healthcare cybersecurity and compliance can be complex. A full-time CISO is a luxury few organizations can afford, but qualified information security leadership is a must. So, what do you do?
A Virtual Chief Information Security Officer (or vCISO) provides the necessary leadership, strategic planning oversight, and guidance required to achieve compliance and minimize security risk to a healthcare organization.
Gap / Baseline Assessments
Identify Your Gaps and Roadmap to Compliance
Achieving readiness or certification on a regulation or framework typically involves a gap assessment. We conduct your gap assessment and provide you with a report and remediation roadmap for frameworks & regulations such as ISO 27001, SSAE18 SOC2, PCI-DSS, NIST-CSF, and many more.
NIST Compliance
Gap Assessment & Implementation Support
The National Institute of Standards and Technology (NIST) promotes a Cybersecurity Framework (CSF) to enable organizations to better manage and reduce cybersecurity risk.The NIST CSF consists of five core functions – Identify, Protect, Detect, Respond, and Recover. We assess organizations against the five core functions and their categories. This assessment reveals gaps between the framework and the client’s actual security program. Addressing these gaps enables clients improve their cybersecurity posture by implementing a robust, comprehensive cybersecurity framework.
PCI Compliance
Painless Payment Compliance Support
Depending on where you are in your compliance journey, you may be familiar with the Payment Card Industry Data Security Standard (PCI DSS). The PCI DSS is a global standard by the PCI Council that provides a baseline of people, process and technology requirements designated to protect payment data and facilitate consistent data security measures.
PatientLock follows a comprehensive approach to assess and maintain your PCI DSS compliance and certification. Our highly qualified team with years of experience in this area will take the right steps needed to ensure your compliance.
CMMC Compliance
Get Ready for CMMC 2.0 Compliance
PatientLock provides CMMC readiness services to healthcare organizations on their path to certification against the CMMC standard.
HIPAA Risk Assessment
HIPAA Compliance Just Got Easier
PatientLock walks you through every step of the HIPAA process, from assessment to implementation and maintenance, telling you exactly what you need to meet expectations. Find out why hundreds of healthcare organizations trust our HIPAA Compliance services.
Our team of cybersecurity and compliance experts simplify HIPAA compliance into a few key steps — saving you time and limiting employee stress while making sure you stay compliant.
Incident Response (IR)
Be Prepared for Your Next Cyber Incident
Incident response is the systematic approach in which an organization handles a cyber incident or a breach. At a minimum, every organization must have a clear and comprehensive incident response plan outlining roles and responsibilities, process and procedures in the event of a cyber incident. Every person involved in executing the incident response must be trained and should have participated in a series of tests of the plan.
PatientLock is your trusted partner in incident response planning and testing. We work with you in the end-to-end process for incident response.
HITRUST Readiness
HITRUST CSF Framework Readiness Service
Achieve your objective in a timely and efficient manner with PatientLock’s HITRUST Readiness Services.
PatientLock will walk you through a Readiness Assessment for the HITRUST CSF Framework, remediate the gaps, and prepare for a successful, certifiable HITRUST Assessment.
HITRUST Readiness is designed to help you achieve HITRUST CSF Framework validation and compliance with regulatory requirements applicable to healthcare organizations.
Penetration Testing
Helping Identify and Remediate Vulnerabilities
Penetration testing is an IT security process where a skilled human resource simulates an authorized attack on a system with its primary goal being to identify any vulnerabilities.
Protecting your organization from cybersecurity threats requires you to take a proactive approach. Healthcare Organizations are prime targets for cyber criminals as the most recent data breach statistics have shown. Penetration testing is a proactive security process which introduces the human element needed in today’s current threat environment. It takes a holistic approach and is tailored to the unique needs of each organization.
Network Security Assessment
Comprehensive Network Analysis
Network Security Assessments are a critical component of maintaining the integrity and confidentiality of your organization’s data and assets. Our team of experts will perform a thorough analysis of your network infrastructure, identifying any potential weaknesses or vulnerabilities. This includes examining your firewalls, routers, switches, and other networking devices to ensure they are properly configured and protected against external threats.
Proactively mitigate risks and protect your business from cyberattacks, data breaches, and other security incidents. Our assessment report will provide recommendations for improving your network security, and our team will work with you to implement these changes and ensure your network is secure.